01 · Orchestration, configuration and owner decisions
SVGThe voyage command follows STAGES, loads role configuration and asks the owner at PLAN, REPAIR, merge and LOCK. Prompts in agents/ take effect only when a command actually loads them.
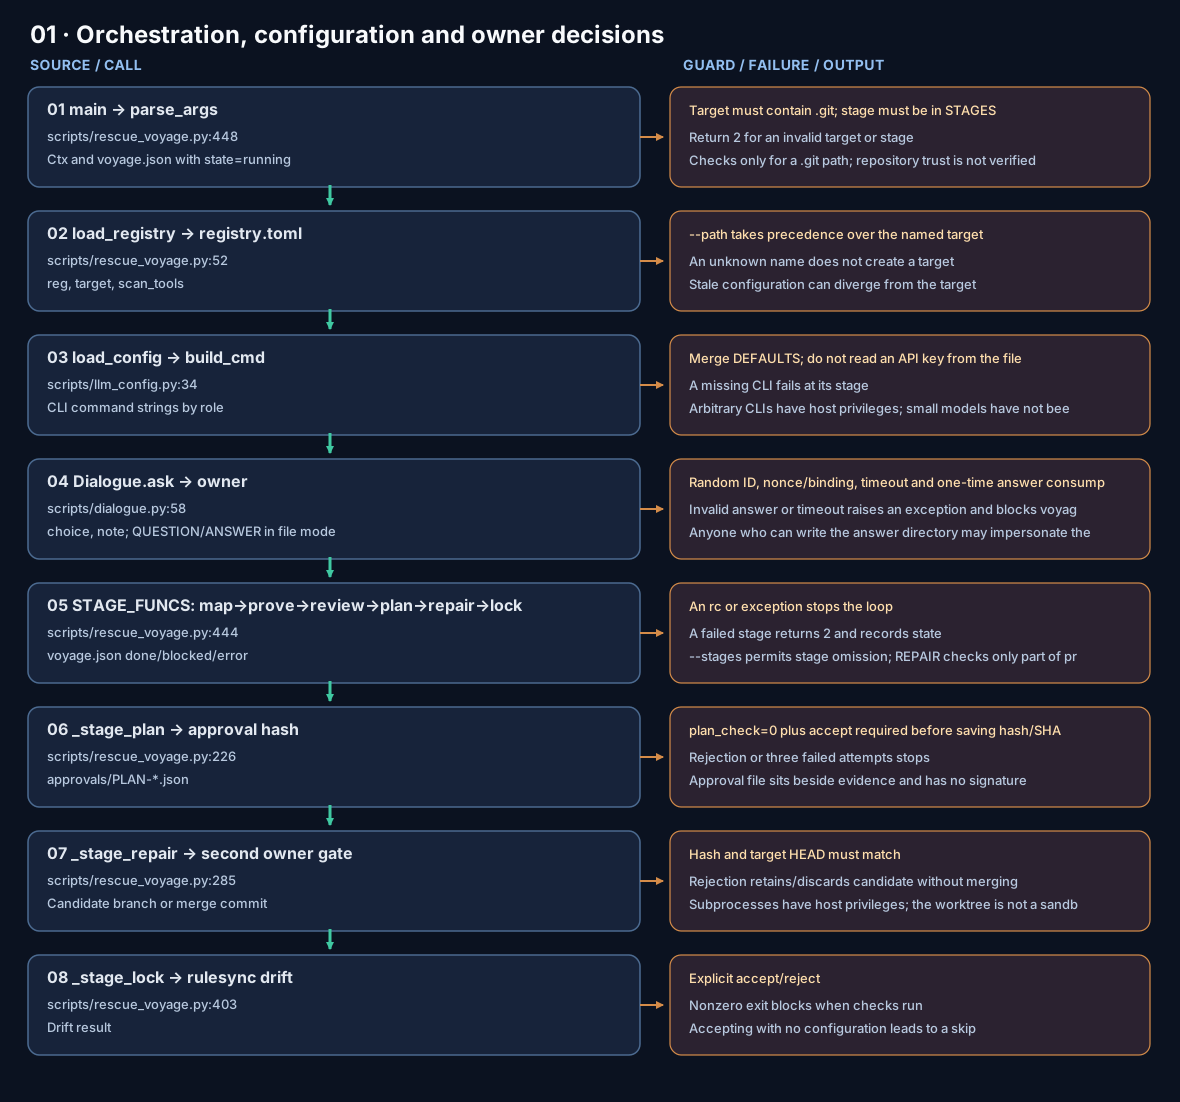
01 · main → parse_argsscripts/rescue_voyage.py:448 · Identify the target, stages, probe and command overrides.
- Guard
- Target must contain .git; stage must be in STAGES
- Output
- Ctx and voyage.json with state=running
- Failure
- Return 2 for an invalid target or stage
- Risk
- Checks only for a .git path; repository trust is not verified
02 · load_registry → registry.tomlscripts/rescue_voyage.py:52 · Get the target name, scanner set, probe and owner mode from the registry.
- Guard
- --path takes precedence over the named target
- Output
- reg, target, scan_tools
- Failure
- An unknown name does not create a target
- Risk
- Stale configuration can diverge from the target
03 · load_config → build_cmdscripts/llm_config.py:34 · Assign write, verify and audit from config.toml or VIBE_LLM_CONFIG.
- Guard
- Merge DEFAULTS; do not read an API key from the file
- Output
- CLI command strings by role
- Failure
- A missing CLI fails at its stage
- Risk
- Arbitrary CLIs have host privileges; small models have not been fully evaluated
04 · Dialogue.ask → ownerscripts/dialogue.py:58 · Record or ask for a decision; never approve automatically.
- Guard
- Random ID, nonce/binding, timeout and one-time answer consumption
- Output
- choice, note; QUESTION/ANSWER in file mode
- Failure
- Invalid answer or timeout raises an exception and blocks voyage
- Risk
- Anyone who can write the answer directory may impersonate the owner
05 · STAGE_FUNCS: map→prove→review→plan→repair→lockscripts/rescue_voyage.py:444 · Run in fixed order even when --stages lists another order.
- Guard
- An rc or exception stops the loop
- Output
- voyage.json done/blocked/error
- Failure
- A failed stage returns 2 and records state
- Risk
- --stages permits stage omission; REPAIR checks only part of preflight itself
06 · _stage_plan → approval hashscripts/rescue_voyage.py:226 · An advisor or template creates the plan; plan_check runs before owner approval.
- Guard
- plan_check=0 plus accept required before saving hash/SHA
- Output
- approvals/PLAN-*.json
- Failure
- Rejection or three failed attempts stops
- Risk
- Approval file sits beside evidence and has no signature
07 · _stage_repair → second owner gatescripts/rescue_voyage.py:285 · Check plan hash and HEAD; ask before execution and again before merge.
- Guard
- Hash and target HEAD must match
- Output
- Candidate branch or merge commit
- Failure
- Rejection retains/discards candidate without merging
- Risk
- Subprocesses have host privileges; the worktree is not a sandbox
08 · _stage_lock → rulesync driftscripts/rescue_voyage.py:403 · The owner decides whether to run drift checks when a target has rulesync.
- Guard
- Explicit accept/reject
- Output
- Drift result
- Failure
- Nonzero exit blocks when checks run
- Risk
- Accepting with no configuration leads to a skip
02 · MAP, PROVE and the evidence path
SVGThis path separates repository mapping, scanners, parsers, baselines and reports. Each tool has an ok/skipped/failed status; scanner output alone does not establish complete coverage.
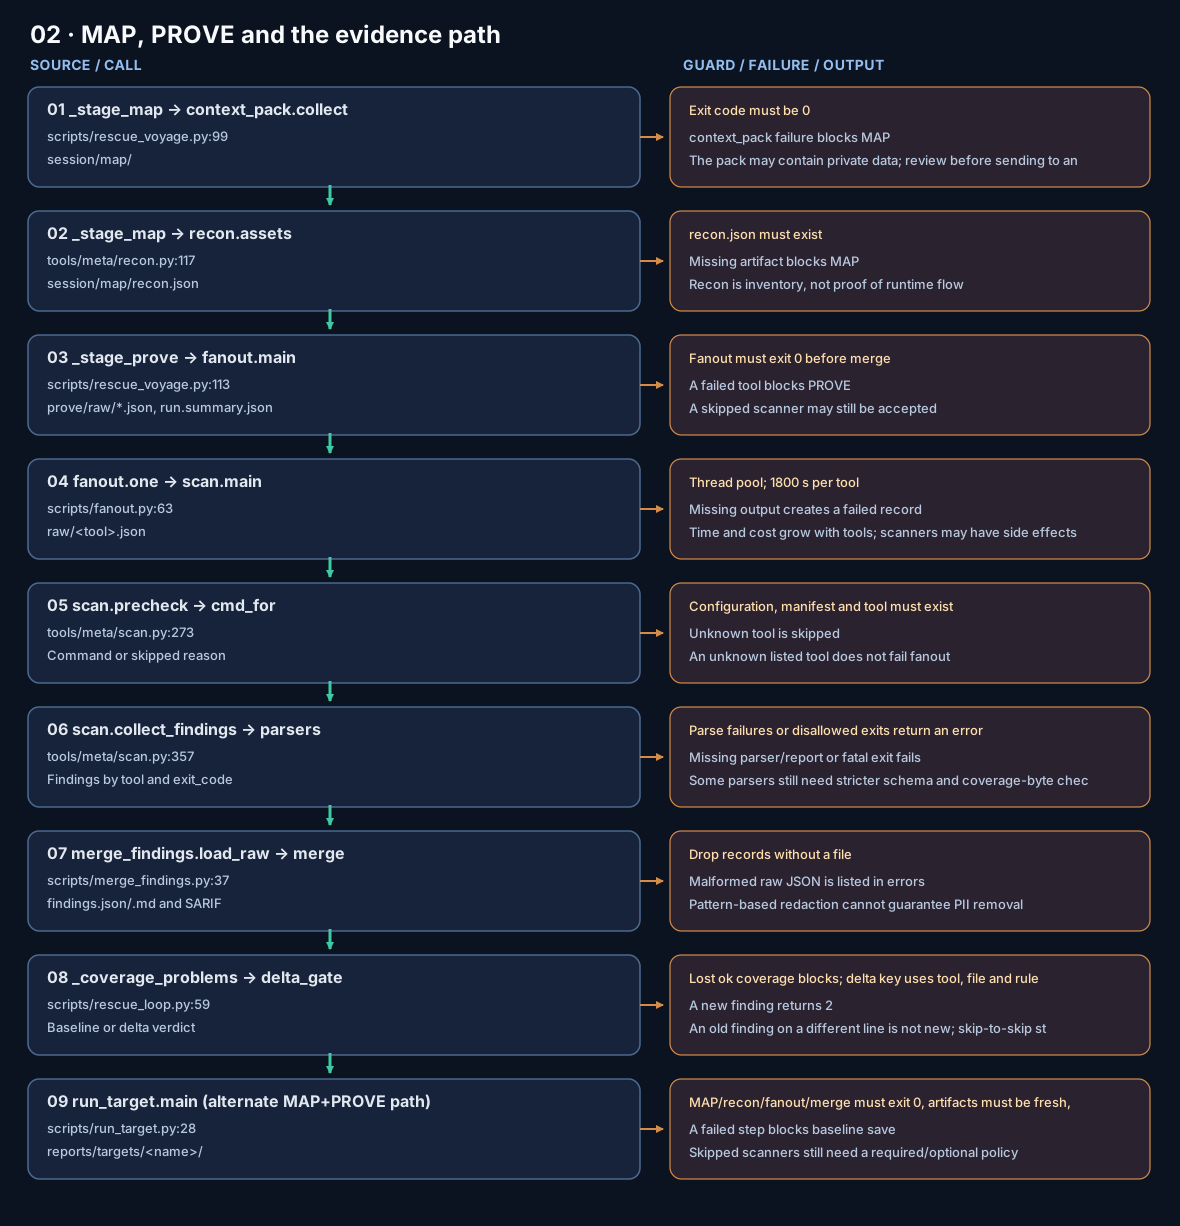
01 · _stage_map → context_pack.collectscripts/rescue_voyage.py:99 · Build a bounded context pack and target inventory.
- Guard
- Exit code must be 0
- Output
- session/map/
- Failure
- context_pack failure blocks MAP
- Risk
- The pack may contain private data; review before sending to an LLM
02 · _stage_map → recon.assetstools/meta/recon.py:117 · Count languages, large files, Git state and agent assets.
- Guard
- recon.json must exist
- Output
- session/map/recon.json
- Failure
- Missing artifact blocks MAP
- Risk
- Recon is inventory, not proof of runtime flow
03 · _stage_prove → fanout.mainscripts/rescue_voyage.py:113 · Select scanners and run them concurrently.
- Guard
- Fanout must exit 0 before merge
- Output
- prove/raw/*.json, run.summary.json
- Failure
- A failed tool blocks PROVE
- Risk
- A skipped scanner may still be accepted
04 · fanout.one → scan.mainscripts/fanout.py:63 · Launch one subprocess per tool in the manifest.
- Guard
- Thread pool; 1800 s per tool
- Output
- raw/<tool>.json
- Failure
- Missing output creates a failed record
- Risk
- Time and cost grow with tools; scanners may have side effects
05 · scan.precheck → cmd_fortools/meta/scan.py:273 · Classify unavailable/skipped tools and construct pinned commands.
- Guard
- Configuration, manifest and tool must exist
- Output
- Command or skipped reason
- Failure
- Unknown tool is skipped
- Risk
- An unknown listed tool does not fail fanout
06 · scan.collect_findings → parserstools/meta/scan.py:357 · Normalize tool output into findings.
- Guard
- Parse failures or disallowed exits return an error
- Output
- Findings by tool and exit_code
- Failure
- Missing parser/report or fatal exit fails
- Risk
- Some parsers still need stricter schema and coverage-byte checks
07 · merge_findings.load_raw → mergescripts/merge_findings.py:37 · Redact text, normalize paths and deduplicate severity.
- Guard
- Drop records without a file
- Output
- findings.json/.md and SARIF
- Failure
- Malformed raw JSON is listed in errors
- Risk
- Pattern-based redaction cannot guarantee PII removal
08 · _coverage_problems → delta_gatescripts/rescue_loop.py:59 · Compare scanner lists/statuses and new findings.
- Guard
- Lost ok coverage blocks; delta key uses tool, file and rule
- Output
- Baseline or delta verdict
- Failure
- A new finding returns 2
- Risk
- An old finding on a different line is not new; skip-to-skip still passes
09 · run_target.main (alternate MAP+PROVE path)scripts/run_target.py:28 · An independent entry point scans a registry target.
- Guard
- MAP/recon/fanout/merge must exit 0, artifacts must be fresh, at least one scanner ok
- Output
- reports/targets/<name>/
- Failure
- A failed step blocks baseline save
- Risk
- Skipped scanners still need a required/optional policy
03 · Prompts, audit and team handoff
SVGThe audit role writes the review when its CLI runs. The fallback template contains real counts but is not a deep audit. Cross-check and number-check are currently advisory.
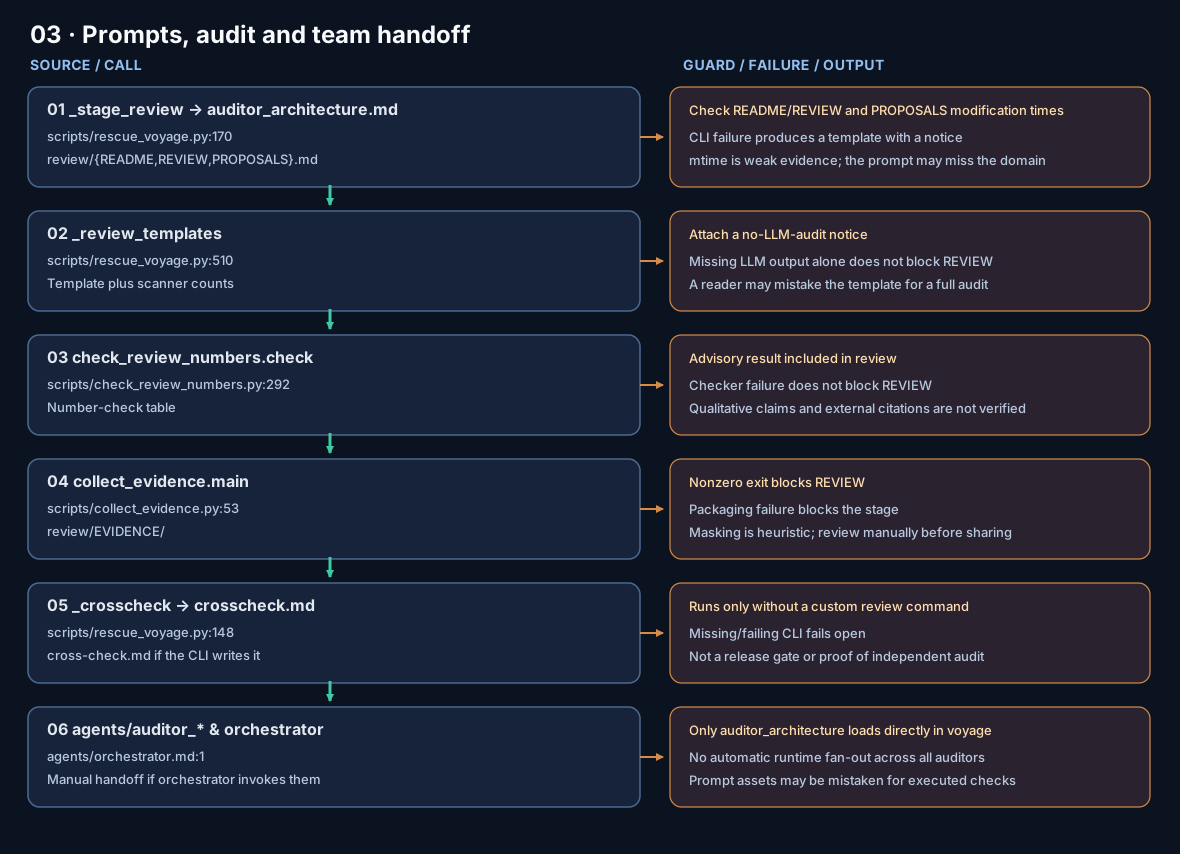
01 · _stage_review → auditor_architecture.mdscripts/rescue_voyage.py:170 · Load the audit prompt through PROMPT_AGENT and invoke review_cmd.
- Guard
- Check README/REVIEW and PROPOSALS modification times
- Output
- review/{README,REVIEW,PROPOSALS}.md
- Failure
- CLI failure produces a template with a notice
- Risk
- mtime is weak evidence; the prompt may miss the domain
02 · _review_templatesscripts/rescue_voyage.py:510 · Provide a fallback when the agent writes no fresh files.
- Guard
- Attach a no-LLM-audit notice
- Output
- Template plus scanner counts
- Failure
- Missing LLM output alone does not block REVIEW
- Risk
- A reader may mistake the template for a full audit
03 · check_review_numbers.checkscripts/check_review_numbers.py:292 · Compare numerical claims with evidence and source.
- Guard
- Advisory result included in review
- Output
- Number-check table
- Failure
- Checker failure does not block REVIEW
- Risk
- Qualitative claims and external citations are not verified
04 · collect_evidence.mainscripts/collect_evidence.py:53 · Collect masked JSON for handoff.
- Guard
- Nonzero exit blocks REVIEW
- Output
- review/EVIDENCE/
- Failure
- Packaging failure blocks the stage
- Risk
- Masking is heuristic; review manually before sharing
05 · _crosscheck → crosscheck.mdscripts/rescue_voyage.py:148 · Have the verify role inspect wrong counts, contradictions and missing evidence.
- Guard
- Runs only without a custom review command
- Output
- cross-check.md if the CLI writes it
- Failure
- Missing/failing CLI fails open
- Risk
- Not a release gate or proof of independent audit
06 · agents/auditor_* & orchestratoragents/orchestrator.md:1 · Specialized prompts describe roles and expected output.
- Guard
- Only auditor_architecture loads directly in voyage
- Output
- Manual handoff if orchestrator invokes them
- Failure
- No automatic runtime fan-out across all auditors
- Risk
- Prompt assets may be mistaken for executed checks
04 · PLAN, candidate, reviewer and rollback
SVGA candidate runs in a worktree and passes scope, probe, scan and reviewer checks before the owner is asked to merge. A post-merge probe can trigger a conditional auto-revert. These are Git gates, not an operating-system sandbox.
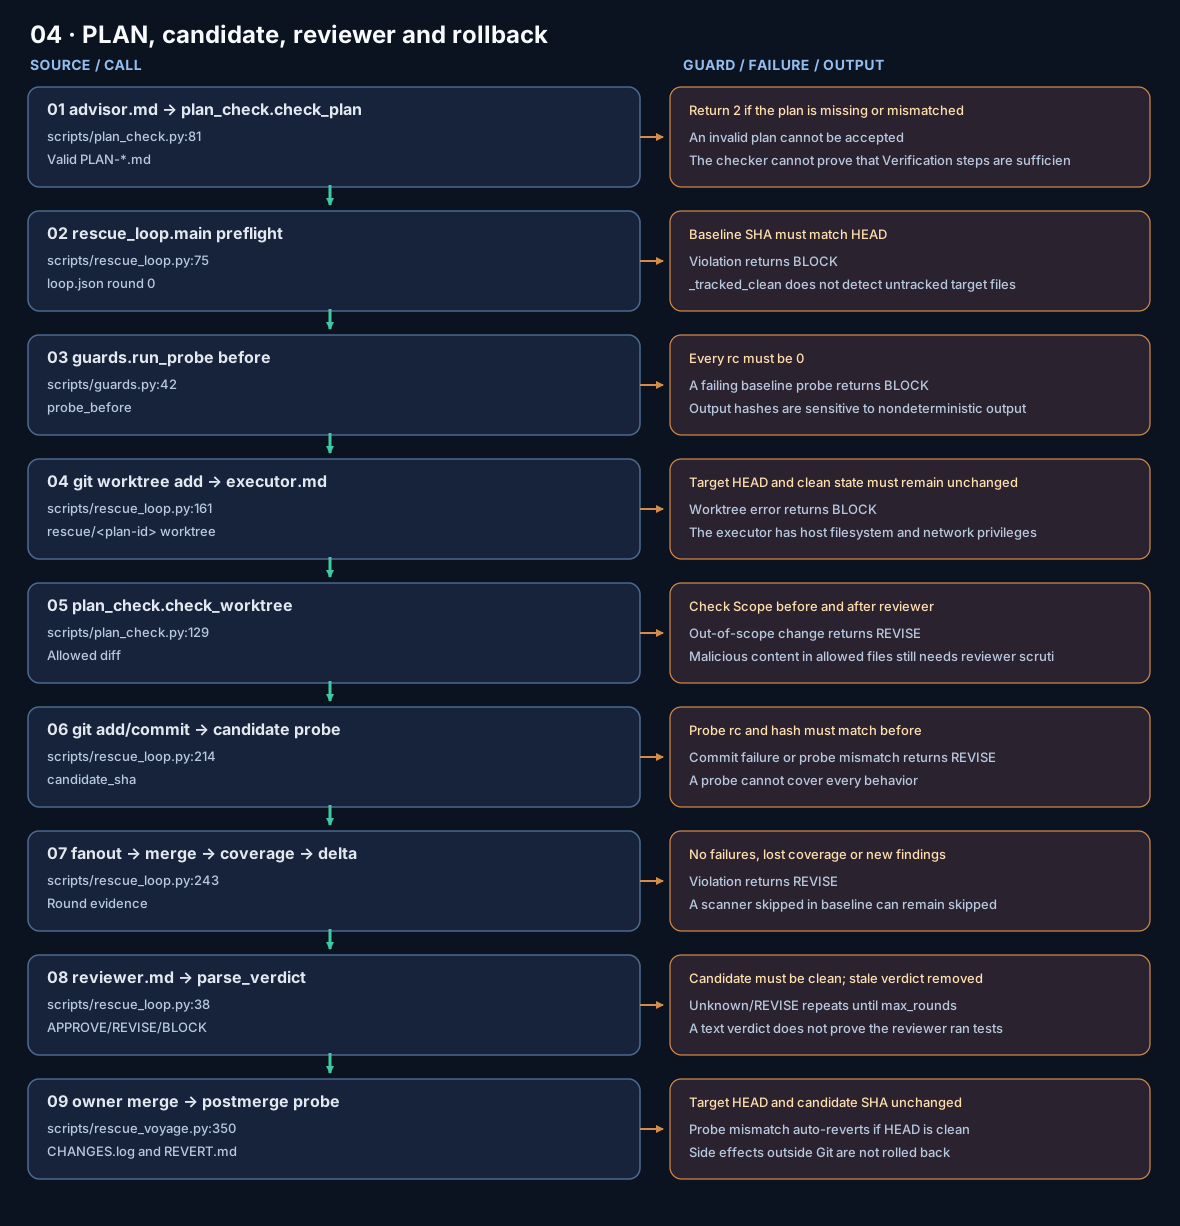
01 · advisor.md → plan_check.check_planscripts/plan_check.py:81 · Check sections, verification per step, Scope and SHA.
- Guard
- Return 2 if the plan is missing or mismatched
- Output
- Valid PLAN-*.md
- Failure
- An invalid plan cannot be accepted
- Risk
- The checker cannot prove that Verification steps are sufficient
02 · rescue_loop.main preflightscripts/rescue_loop.py:75 · Check baseline, probe, clean target, HEAD and coverage.
- Guard
- Baseline SHA must match HEAD
- Output
- loop.json round 0
- Failure
- Violation returns BLOCK
- Risk
- _tracked_clean does not detect untracked target files
03 · guards.run_probe beforescripts/guards.py:42 · Capture probe rc and stdout/stderr hashes.
- Guard
- Every rc must be 0
- Output
- probe_before
- Failure
- A failing baseline probe returns BLOCK
- Risk
- Output hashes are sensitive to nondeterministic output
04 · git worktree add → executor.mdscripts/rescue_loop.py:161 · Create a candidate branch and invoke the writer.
- Guard
- Target HEAD and clean state must remain unchanged
- Output
- rescue/<plan-id> worktree
- Failure
- Worktree error returns BLOCK
- Risk
- The executor has host filesystem and network privileges
05 · plan_check.check_worktreescripts/plan_check.py:129 · Require changed filenames to stay within Scope.
- Guard
- Check Scope before and after reviewer
- Output
- Allowed diff
- Failure
- Out-of-scope change returns REVISE
- Risk
- Malicious content in allowed files still needs reviewer scrutiny
06 · git add/commit → candidate probescripts/rescue_loop.py:214 · Commit the candidate for a real merge and compare probes.
- Guard
- Probe rc and hash must match before
- Output
- candidate_sha
- Failure
- Commit failure or probe mismatch returns REVISE
- Risk
- A probe cannot cover every behavior
07 · fanout → merge → coverage → deltascripts/rescue_loop.py:243 · Scan candidate with the baseline scanner set.
- Guard
- No failures, lost coverage or new findings
- Output
- Round evidence
- Failure
- Violation returns REVISE
- Risk
- A scanner skipped in baseline can remain skipped
08 · reviewer.md → parse_verdictscripts/rescue_loop.py:38 · Have an independent verify role write a clear verdict.
- Guard
- Candidate must be clean; stale verdict removed
- Output
- APPROVE/REVISE/BLOCK
- Failure
- Unknown/REVISE repeats until max_rounds
- Risk
- A text verdict does not prove the reviewer ran tests
09 · owner merge → postmerge probescripts/rescue_voyage.py:350 · Owner approves merge; compare SHA and run a post-merge probe.
- Guard
- Target HEAD and candidate SHA unchanged
- Output
- CHANGES.log and REVERT.md
- Failure
- Probe mismatch auto-reverts if HEAD is clean
- Risk
- Side effects outside Git are not rolled back
05 · Multilanguage logic atlas and MIT release
SVGThe target analyzer builds a static graph; this repository explorer indexes every Python function in the harness itself. A public release must use a clean source snapshot, not the old Git history.
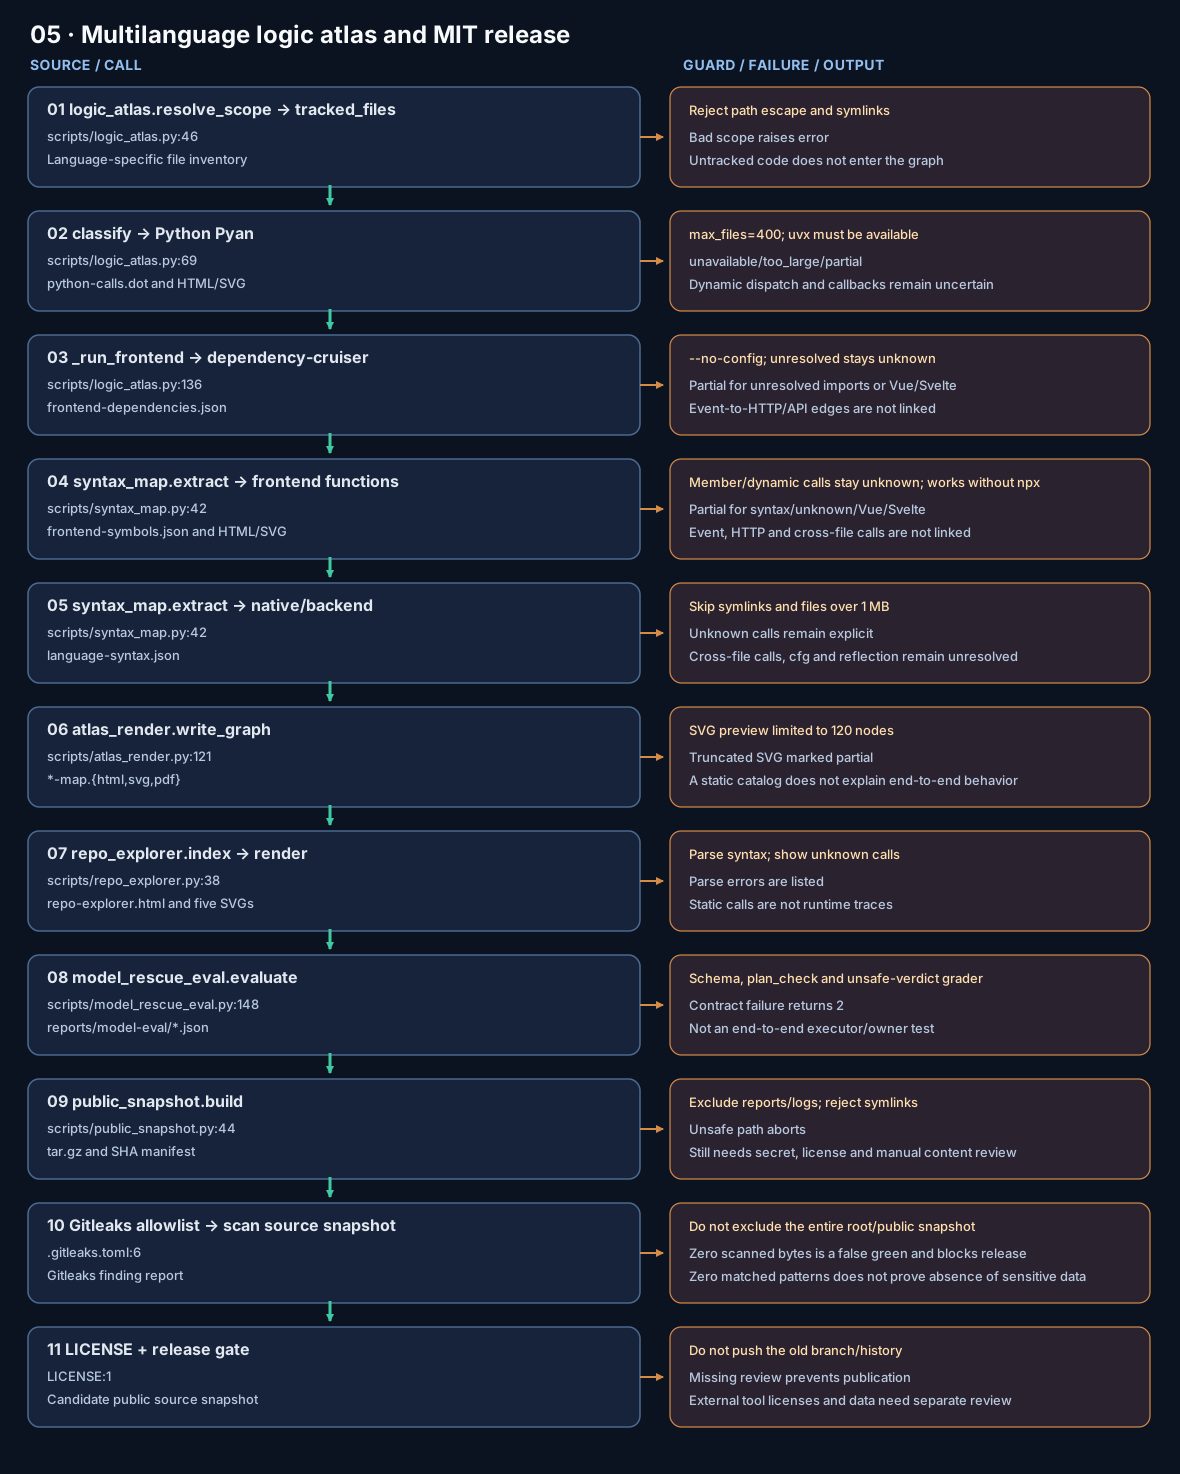
01 · logic_atlas.resolve_scope → tracked_filesscripts/logic_atlas.py:46 · Constrain scope to the target and read only Git-tracked regular files.
- Guard
- Reject path escape and symlinks
- Output
- Language-specific file inventory
- Failure
- Bad scope raises error
- Risk
- Untracked code does not enter the graph
02 · classify → Python Pyanscripts/logic_atlas.py:69 · Build a static Python call graph with pinned Pyan.
- Guard
- max_files=400; uvx must be available
- Output
- python-calls.dot and HTML/SVG
- Failure
- unavailable/too_large/partial
- Risk
- Dynamic dispatch and callbacks remain uncertain
03 · _run_frontend → dependency-cruiserscripts/logic_atlas.py:136 · Build JS/TS import graph without executing target configuration.
- Guard
- --no-config; unresolved stays unknown
- Output
- frontend-dependencies.json
- Failure
- Partial for unresolved imports or Vue/Svelte
- Risk
- Event-to-HTTP/API edges are not linked
04 · syntax_map.extract → frontend functionsscripts/syntax_map.py:42 · Extract JS/TS/JSX/TSX functions, arrow variables and direct same-file calls.
- Guard
- Member/dynamic calls stay unknown; works without npx
- Output
- frontend-symbols.json and HTML/SVG
- Failure
- Partial for syntax/unknown/Vue/Svelte
- Risk
- Event, HTTP and cross-file calls are not linked
05 · syntax_map.extract → native/backendscripts/syntax_map.py:42 · Extract Rust/Go/Java/PHP/C# symbols and same-file calls.
- Guard
- Skip symlinks and files over 1 MB
- Output
- language-syntax.json
- Failure
- Unknown calls remain explicit
- Risk
- Cross-file calls, cfg and reflection remain unresolved
06 · atlas_render.write_graphscripts/atlas_render.py:121 · Export offline HTML/SVG/PDF with a full node/edge/unknown HTML catalog.
- Guard
- SVG preview limited to 120 nodes
- Output
- *-map.{html,svg,pdf}
- Failure
- Truncated SVG marked partial
- Risk
- A static catalog does not explain end-to-end behavior
07 · repo_explorer.index → renderscripts/repo_explorer.py:38 · Index all functions, variables and calls in the harness without a 120-node cap.
- Guard
- Parse syntax; show unknown calls
- Output
- repo-explorer.html and five SVGs
- Failure
- Parse errors are listed
- Risk
- Static calls are not runtime traces
08 · model_rescue_eval.evaluatescripts/model_rescue_eval.py:148 · Smoke-test MAP/PLAN/REVIEW on synthetic fixtures through a budget model gateway.
- Guard
- Schema, plan_check and unsafe-verdict grader
- Output
- reports/model-eval/*.json
- Failure
- Contract failure returns 2
- Risk
- Not an end-to-end executor/owner test
09 · public_snapshot.buildscripts/public_snapshot.py:44 · Package fresh source without old Git history or reports.
- Guard
- Exclude reports/logs; reject symlinks
- Output
- tar.gz and SHA manifest
- Failure
- Unsafe path aborts
- Risk
- Still needs secret, license and manual content review
10 · Gitleaks allowlist → scan source snapshot.gitleaks.toml:6 · Scan extracted source and verify scanned bytes are nonzero.
- Guard
- Do not exclude the entire root/public snapshot
- Output
- Gitleaks finding report
- Failure
- Zero scanned bytes is a false green and blocks release
- Risk
- Zero matched patterns does not prove absence of sensitive data
11 · LICENSE + release gateLICENSE:1 · Prepare source for MIT release.
- Guard
- Do not push the old branch/history
- Output
- Candidate public source snapshot
- Failure
- Missing review prevents publication
- Risk
- External tool licenses and data need separate review
All Python functions
Search functions, files, calls, variables and fields. Select a function to inspect callers, callees, parameters, local variables, fields and its docstring. Source lines are evidence; the graph does not establish runtime branches.
Select a function on the left.
Config · prompts · rules · tests
This inventory comes from the working tree at generation time. Open each file to inspect its contents and execution permissions; its presence does not prove runtime use.